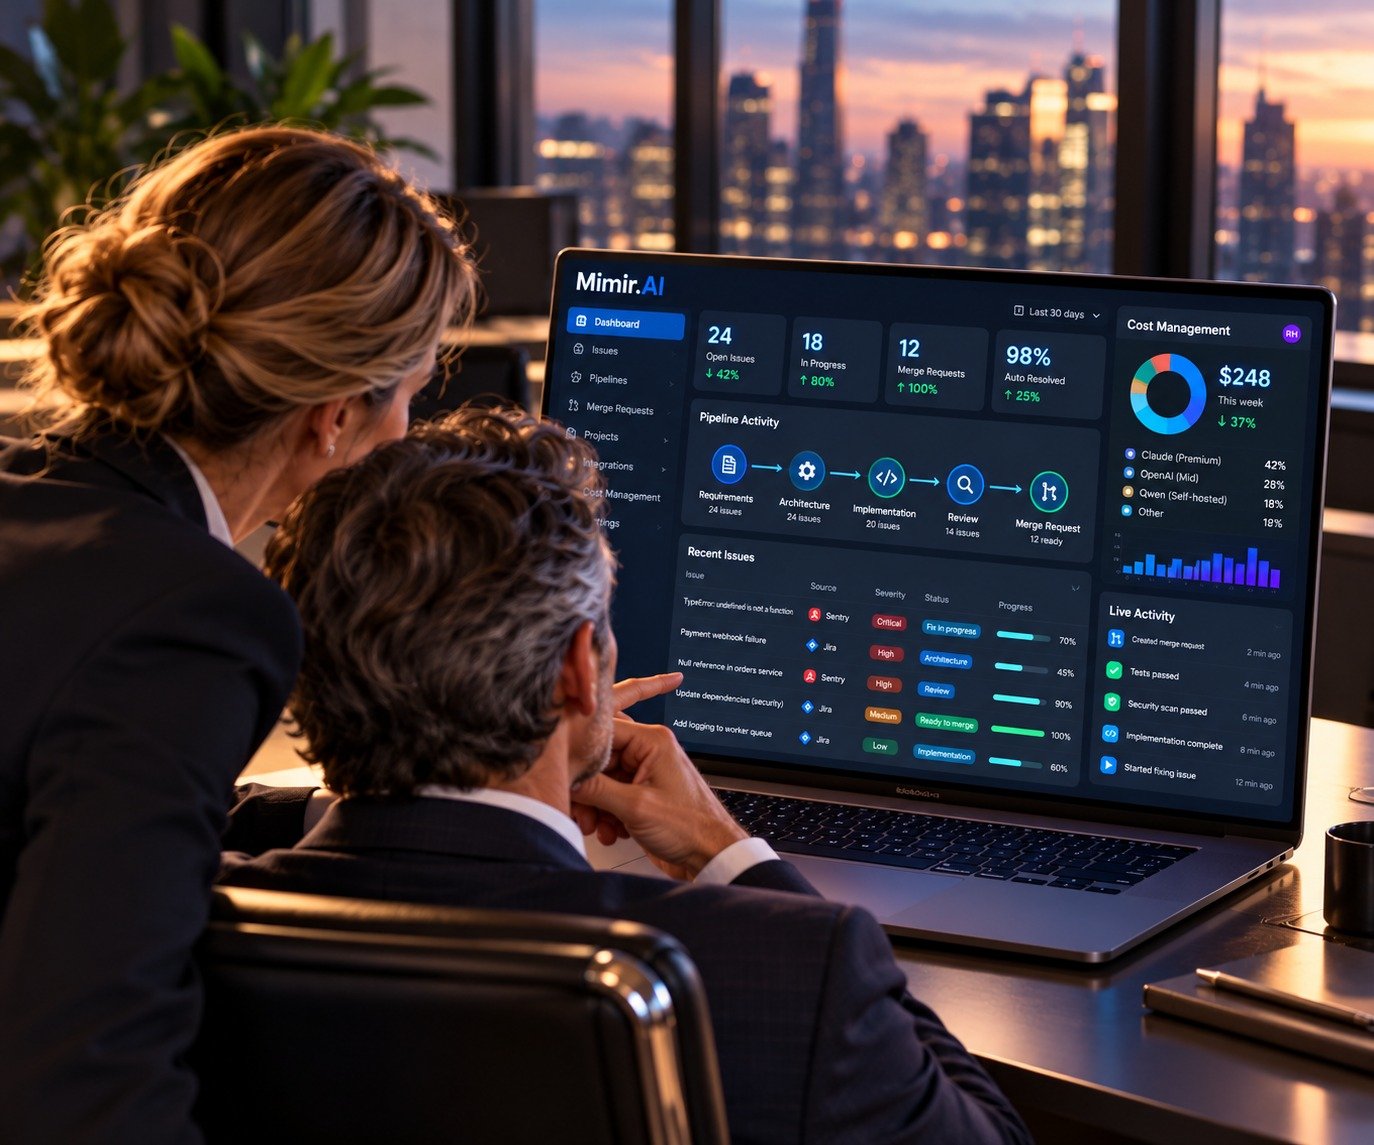
AI agents do the work.
You approve the fix.
Mimir.AI connects Sentry, Jira and GitLab, hands each error or ticket to sandboxed coding agents, and brings you a tested, reviewed merge request. Nothing merges until your team says so.
Your agents take each issue from alert to merge request
Every step is recorded, budgeted and visible. People step in where judgement matters: approving plans, answering agent questions and merging.
Everything between the bug report and the release branch
Coding agents
Claude Code or Codex in ephemeral Docker or Kubernetes sandboxes with the right toolchain for each repository.
Agents →Workflows
Eight built-in templates, from quick fixes to plan-first stories, with approval gates and spend limits.
Workflows →Review & merge
Version-aware branch plans, side-by-side diffs, one-click merge and automatic carry-forward to newer branches.
Review & merge →Board & sprints
One work list across Sentry, Jira, GitLab and Mimir, with a two-way synced board, backlog and sprints.
Board →Chat & knowledge
Ask about your code and tickets, turn a spec into a reviewed ticket plan, and ground answers in your documents.
Chat & knowledge →Cost control
Route each task by difficulty and risk, cap budgets per run, workflow and day, and see where the spend went.
Cost control →Autonomy with guardrails you set
Mimir is designed so an agent can never quietly push to production.
- Approval before write. Automatic triggers must pass a human approval step before any agent writes code.
- You merge. Merge requests respect GitLab approvals, discussions and CI blockers.
- Budgets everywhere. Per-run, per-workflow and daily spend caps, plus concurrency limits.
- Secrets stay secret. Credentials are encrypted with AES-256-GCM and never returned to the browser.
Humans approve.
Mimir handles the rest.
Book a demo
One loop from error to tested fix
Mimir watches your delivery tools, runs configurable workflows that mix quick model calls, sandboxed coding agents and human approvals, then hands the result to testing.
- 1
Ingest
Sentry errors, Jira issues, human merge requests, failing GitLab pipelines and Mimir's own board items arrive in one work list. Backfill, background sync and signed webhooks keep it current.
sentry.issue.createdjira.issue.transitionedgitlab.pipeline.failedboard.item.moved - 2
Triage
The Triage agent scores difficulty and risk from 1 to 10, saves the assessment, fills version hints and comments on the ticket. It runs cheaply, without a coding container.
- 3
Plan and approve
Plan-first workflows investigate and propose a fix. You approve it, edit it or reject it with feedback, and can adjust the target branch before any code is pushed.
- 4
Implement
A coding agent clones the planned base, works on its own branch in a sandbox, runs setup and verification commands and pushes. You can message it, and it can ask you questions mid-run.
- 5
Review
When difficulty or risk is 4 or above, a review agent checks the change and can send it back for another fix, within a bounded number of attempts. Simple work skips the extra review cost.
- 6
Merge
Open the review page for diffs, CI status and blockers, then merge, squash or schedule merge-when-pipeline-succeeds. GitLab's rules still apply.
- 7
Hand off and carry forward
Mimir moves the ticket to your test lane, resolves the Sentry error, and ports the fix into newer open release branches and development.
Three moments that need you
Approval steps
Review the plan or output, edit it, then approve or reject. Pending approvals show in the sidebar and dashboard.
Agent questions
When an agent asks something, it shows as "Needs your answer". Reply from the run page, or let it continue on its own judgement after the timeout.
Merging
Every merge is a person's decision, made in Mimir or in GitLab. Hand-off only starts once GitLab confirms the merge.
What's coming next
These are planned and not part of the current release.
A team of agents on every project
Assign work to an agent the way you assign it to a colleague. It picks up the ticket, works in an isolated sandbox and reports back, while the human assignee stays on the ticket.
What an agent run looks like
Each run moves through clear states and leaves a full timeline of tool calls, usage and cost.
Runs can also end as NoChanges, Failed or Cancelled, so "nothing to do" never looks like success.
OrderDto. Keep the field nullable for older clients?
Project agents
Name an agent, pick its workflow, default model and instructions, and choose which issue types and events it reacts to.
Triage and Tester presets
Triage reacts to new bugs and errors. Tester picks up items moved to In Review, tests the open MR and sends failures back to In Progress.
Read or write
Read runs investigate and return structured output without pushing. Write runs commit to a work branch, reused across fix attempts.
The right toolchain for every repository
Agents run in ephemeral containers on your Docker host or as Kubernetes Jobs. Mimir picks the environment from .mimir/environment.yml or by detecting your project files.
- Pinned tool versions through mise and your version files.
- Package caches per repository, trimmed to a size you set.
- Concurrency limits globally, per project and per person.
- A watchdog on time, heartbeat and executor health, with clean cancellation.
- CI on demand. Agents can run your GitLab pipeline on a scratch branch and read failed-job logs.
Start from a template, shape it to your team
Workflows are ordered steps that combine quick model calls, coding agents, human approvals and integration actions. Each run snapshots its definition, so editing a workflow never changes work in flight.
Pick a template to see its steps
Run on demand or when something happens
Start a workflow from any item, or let events start it. Every trigger and its outcome is recorded, including why a run didn't start.
Safe by construction
- Approval before write is enforced for every automatic trigger.
- Bounded loops. Retries and jumps are capped between 1 and 20 attempts, 3 by default.
- Spend limits per workflow and per day, plus a cap on active automatic runs.
- No runaway chains. An agent never reacts to its own board moves.
- Blocked items wait. Work blocked by another ticket isn't picked up automatically.
Stay in charge of every execution
Approve or reject
Edit the output before approving, or reject with feedback.
Retry or rerun
Rerun with the same choices, or pick a stronger model.
Revise
Send an existing MR back with feedback or conflict guidance.
Cancel
Stop a run cleanly, singly or in bulk.
The right branch, a clear diff, one click to merge
Mimir knows your branching model and release versions, so fixes land where they belong and reach every branch that needs them.
See the plan before any code moves
Before a run, Mimir previews the base, target and work branch with its confidence and reasons. It refuses to write into a released version and suggests the next open fix line instead.
SemVer, four-part and CalVer version schemes are supported.
Everything you need to decide, in one place
Side-by-side diffs
Changed files open in a full code editor view, with binary and oversized files clearly marked.
Live merge checks
Draft state, CI status, mergeability, unresolved discussions and the original work item, straight from GitLab.
Merge your way
Squash, remove the source branch or merge when the pipeline succeeds. Conflicts come back with details, not a generic error.
One fix, every branch that needs it
After the merge, Mimir ports the fix through newer open branches and finally development. Choose merge or cherry-pick for each hop. Conflicts start a resolve workflow that asks for your approval.
Straight to QA, exactly once
- Moves the ticket to your test lane or Jira testing status, optionally into the active sprint.
- Closes the loop on errors. Sentry errors get a linked testing ticket, a comment and resolution.
- No duplicates. Merge button and webhook can race safely; only one testing ticket is created.
All your work in one place, still in sync with Jira
A single work list across Sentry, Jira, GitLab and Mimir, plus a board, backlog and sprints that write back to Jira.
Unified work list
Filter by project, source, severity, status, type, assignee or "mine", and see each item's latest workflow at a glance.
Board and backlog
Drag to rank and move cards. Lanes map to Jira statuses, with optional work-in-progress warnings.
Sprints
Plan, start and complete sprints. Unfinished work carries over; completed work stays in sprint history.
Hierarchy and links
Epics, stories, tasks, bugs and sub-tasks, with blocks and relates-to links. Blocked items aren't picked up automatically.
Bulk changes
Move many items at once: lane, sprint, assignee, priority, agent or position.
Activity and files
Field history, comments and run activity on every item, with attachments up to 25 MiB.
Local work is never lost
If Jira rejects a write, Mimir keeps your change, shows the sync error and lets you push again.
| Policy | Ticket is created |
|---|---|
| OnImport | When a new error arrives by webhook |
| OnFix | When a fix is started |
| OnMerge (default) | When the fix is merged and handed to testing |
Think it through, then turn it into work
Chat with an assistant that can read your tickets, runs, code and documents. When an idea is ready, it proposes tickets for you to review before anything is created.
Real answers, streamed, with the tools to back them
- Tied to a project or ticket, with conversations, files and cost saved.
- Grounded in your systems: issues, board, runs, code symbols, package registries and knowledge.
- Code-aware sandboxes can read and run your checked-out code, and never push.
| Runtime | How it runs |
|---|---|
| Mimir | Workspace model keys through the Mimir gateway, with Mimir tools |
| Anthropic key | Your own API key, with PDF and image input |
| Claude Code | A sandbox on your personal Claude subscription |
| Coding Plan | A sandbox on your Alibaba Coding Plan |
The assistant suggests. You decide.
Ticket proposals
New tickets and updates arrive as editable cards. Nothing is created until you click.
Plans of up to 80 tickets
Parents, dependencies, estimates and labels, checked for loops and created once, in order.
Refine with AI
Open any ticket in chat and see proposed changes against its current fields.
Your documents, searchable by meaning
Upload specs, runbooks and decks up to 50 MiB. Mimir combines keyword and semantic search and cites the document, section and page.
"Plan from this document" turns a spec into a reviewed ticket plan.
A map of your codebase for people and agents
Mimir indexes each repository's symbols and references, then builds a ranked code map that fits a token budget, 6,000 tokens by default.
- Search symbols and follow definitions, calls and references.
- One index per repository, shared across projects.
- Honest gaps. Agents are told when no index exists rather than guessing.
Spend premium models only where they matter
Mimir scores each piece of work, routes it by your rules and caps spend at every level, so routine fixes stay cheap and hard problems get the attention they need.
How Mimir treats a piece of work
Move the sliders to see how difficulty and risk change the routing band, agent effort and whether the extra review loop runs.
Scores come from a manual label, the saved triage assessment, a cheap classifier or a heuristic fallback, and the source is recorded.
- Complexity band
- Moderate
- Agent effort
- Medium
- Review loop
- Runs
- Reviewer
- Different provider
Routing rules
Ordered rules match source, severity, issue type, labels, complexity and step role, with fallbacks if a model is unavailable.
Budgets at every level
A spend cap per agent run, per workflow and per day, plus limits on concurrent and repeated runs.
Escalate when stuck
When a run struggles, Mimir suggests a stronger model, and a rule can rerun the workflow automatically.
See exactly where the money went
Usage by day, model, project and workflow over any period up to a year, with tokens, cache use and merge-request outcomes.
Subscription estimates are kept separate from actual billed cost.
Workspace keys or personal plans
Use shared organisation keys, or let people run on their own Claude subscription, Anthropic key or Alibaba Coding Plan.
Built for teams that answer to auditors
Single sign-on, encrypted credentials, organisation isolation and roles that separate who can look, who can operate and who can merge.
Sign-in
Keycloak OpenID Connect. Tokens stay in an encrypted, HttpOnly session cookie and never reach browser scripts.
Encrypted credentials
Integration and model keys are encrypted with AES-256-GCM. The interface only shows whether a secret is set.
Organisation isolation
Every record belongs to one organisation, and reads, writes and searches are scoped to it.
Signed webhooks
Sentry signatures, GitLab tokens and tokenised Jira URLs are checked on every incoming event.
Scoped agents
Each run gets its own callback token and, where used, its own budget-limited model key, removed when the run ends.
Safe exports
Project configuration exports never include credentials, tokens, webhook secrets or work history.
The right access for everyone
Invite partners and contractors to single projects as guests. Approvals, merges and configuration stay with your organisation.
| Role | Can |
|---|---|
| Owner | Everything an Admin can, plus transfer ownership |
| Admin | Manage members, provider keys, model routing and agent limits |
| Member | Work across all projects: tickets, workflows, approvals and merges |
| Guest · Viewer | View an invited project's board, tickets and runs |
| Guest · Editor | Viewer, plus create, edit and move tickets |
| Guest · Operator | Editor, plus start, cancel and retry runs |
Runs on your infrastructure
Deploy with Helm and OpenTofu on Kubernetes, with PostgreSQL, a model gateway and optional local embeddings. Agents run as Kubernetes Jobs or on Docker.
- Approval before write on every automatic workflow.
- Sandboxed execution, with resource and image limits you control.
- Chat sandboxes never push changes to your repositories.
Works with the tools you already run
Guided setup for each connection, with the scopes it needs, a test button and clear webhook status.
GitLab
- Multiple repositories per project, shared across projects
- Automatic webhook registration
- Branches, MRs, review comments, CI and failed-job logs
- Merge, schedule, retarget and close
Jira
- Backfill, background sync and webhooks
- Two-way board, comments and attachments
- Sprints, story points and version fields
- Assignee matching to Mimir users
Sentry
- Multiple Sentry projects per Mimir project
- Stack traces, breadcrumbs and release context
- Signed webhooks
- Errors resolved after a merged fix
Your choice of model provider
Know when you're needed
Browser notifications for approvals and agent questions, and live counters in the sidebar.
Copy a project setup in minutes
Export a project's settings, repositories, board lanes, workflows and agents as JSON. Preview an import to catch conflicts before applying it.
Monorepos without duplication
Link one repository to several projects with a single webhook and code index. Events Mimir can't place wait in a "Needs a project" queue, and your choice is remembered.
See your own backlog worked by agents
We'll connect a sandbox project to your Sentry, Jira and GitLab and walk through a real fix, from error to approved merge request.
Thanks,
Sending your request…
What the demo covers
- Connecting your tools and importing a slice of real work.
- A live agent run from triage to merge request.
- Approvals, review and merge as your team would use them.
- Routing and budgets tuned to your model providers.
- Deployment options for your Kubernetes or Docker estate.
mimir.rgsit.com